Deception Technology: Honeypots and Honeytokens That Catch Intruders
An alert with almost no false positives
Every detection method fights the same enemy: noise. A SIEM rule that flags unusual PowerShell has to distinguish a real attack from the hundred legitimate admin scripts that run every day, and that ambiguity is why analysts drown in alerts they cannot trust. Deception technology sidesteps the problem entirely. It works by planting assets that have exactly one property in common — no legitimate user or process has any reason to touch them. A fake credential, a decoy file server, a database record that only exists as bait. The moment something interacts with one, you do not have a suspicious event to investigate. You have an intruder.
This inverts the usual detection logic. Instead of trying to recognize malicious behavior against a backdrop of normal activity, you create tripwires where any activity at all is abnormal by definition. The result is one of the few detection sources with a naturally near-zero false-positive rate. That property makes deception a powerful complement to conventional monitoring, especially for catching the post-compromise phase — lateral movement, reconnaissance, credential theft — where an attacker who already slipped past the perimeter is hardest to spot.
Honeypots, honeytokens, and honeynets
The field spans a spectrum from full decoy systems to single planted artifacts. Each catches a different stage of intrusion.
- Honeytokens are the smallest and often the most useful unit: a single fake artifact designed to be found and used. A set of fake credentials in a config file, a bogus API key, a decoy AWS access key, a database row with a distinctive fake customer name, a document that beacons when opened. They cost almost nothing to deploy and can be scattered widely.
- Honeypots are decoy systems that look like real targets — a fake RDP server, a phony database, a simulated file share — instrumented to log everything an attacker does to them. They catch reconnaissance and exploitation attempts against services that appear vulnerable but hold nothing real.
- Honeynets are whole decoy environments: multiple interconnected honeypots that mimic a real network segment, letting you observe an attacker move laterally and revealing their tooling and objectives in depth.
There is also a classic distinction between low-interaction decoys, which merely emulate a service enough to record a connection attempt, and high-interaction ones, which run real (isolated) systems the attacker can fully engage. Low-interaction is cheap, safe, and easy to scale but reveals little. High-interaction yields rich intelligence about attacker behavior but demands careful isolation so the decoy cannot become a real foothold.
Honeytokens are the fastest win
For most organizations, honeytokens deliver the highest return for the least effort and risk, because they require no separate infrastructure — you salt your existing environment with bait. The scenarios that reliably fire on real intrusions:
- Fake credentials in memory and config. Attackers who land on a host routinely scrape credentials from memory, browsers, and configuration files. A planted set of fake domain credentials that triggers an alert the instant someone attempts to authenticate with them is a direct signal that credential theft is underway.
- Decoy cloud keys. An access key that grants no real permissions but generates a log event the moment it is used tells you an attacker is probing your cloud environment — and exactly which host leaked it.
- Canary documents. A file named to attract attention —
passwords.xlsx,Q4_layoffs.docx— that phones home with the opener's IP when accessed. Any interaction means someone is rummaging where they should not be. - Database honeytokens. A fake record with a unique marker; if that marker ever appears in exfiltrated data, breach-monitoring feeds, or an unexpected query, you have proof of unauthorized access and a way to trace it.
The engineering discipline is placement and instrumentation. A honeytoken only works if it is discoverable by an attacker doing normal reconnaissance, indistinguishable from a real asset, and wired to an alert that reaches your security operations team immediately. A token nobody wires to an alert is just a lie you told yourself.
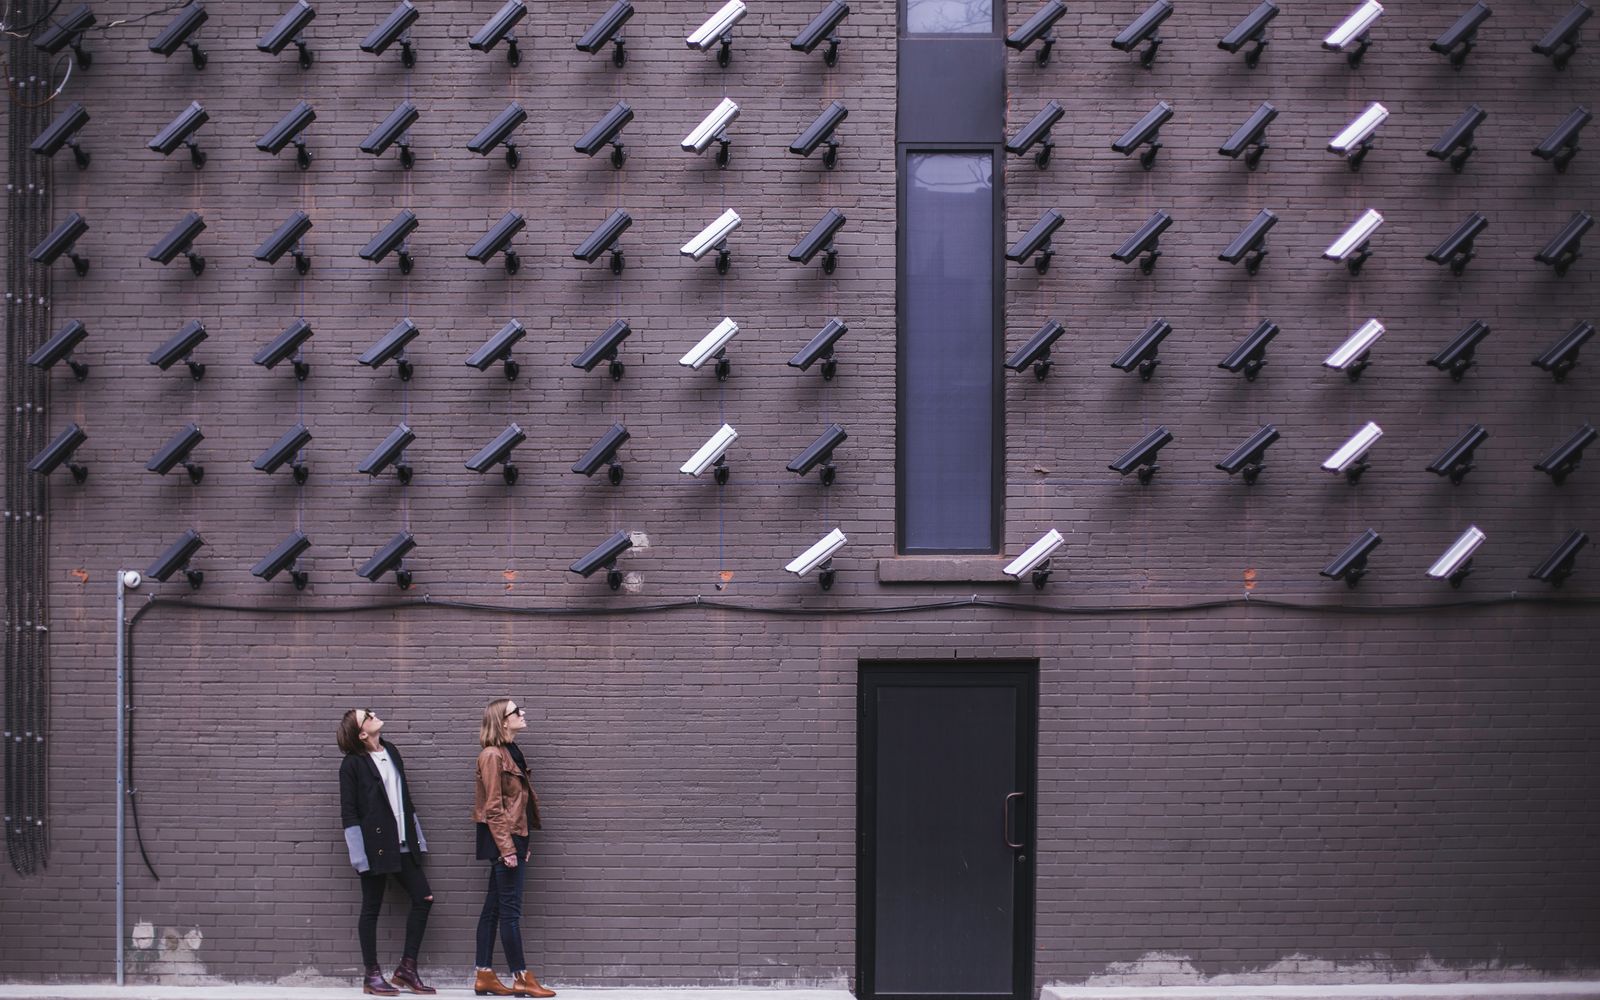
 Figure: deception salts the real environment with decoys — because no legitimate workflow touches them, a single interaction becomes a high-confidence signal of an intruder already inside.
Where deception fits in the defense stack
Deception is not a replacement for endpoint detection, network monitoring, or identity controls — it is a layer that catches what they miss, and it is worth being precise about what it does and does not do.
Its strengths are specific. It excels at detecting the post-breach activity that evades signature-based tools: an attacker already inside, moving laterally, harvesting credentials, and hunting for data. Because the signal is behavioral (someone touched the bait) rather than signature-based, it catches novel tooling and living-off-the-land techniques that have no detection signature at all. It also buys time — an attacker who wastes hours on a convincing honeynet is an attacker not touching your production systems, and every action they take against the decoy is intelligence about their intent.
Its limits are equally clear. Deception detects intruders who interact with the decoys; a targeted attacker who moves straight to a known objective may never trip one. Coverage depends on placing bait where attackers actually look, which requires understanding their tradecraft. And decoys demand maintenance — a honeypot running obviously outdated services, or credentials that no longer match your naming conventions, signals "trap" to a careful adversary. Deception raises the cost and detection probability of an intrusion; it does not guarantee interception.
Turning a trip into a response
A deception alert is high-fidelity but not self-resolving. Because the false-positive rate is so low, these alerts should route to the top of the queue and trigger a defined workflow rather than a shrug.
- Treat it as a confirmed indicator, not a maybe. A honeytoken firing is presumptive evidence of compromise. Skip the "is this real?" triage that consumes other alerts and move directly to scoping.
- Pivot to the source. The alert tells you which host used the fake credential or opened the canary. That host is your starting point for identifying the actual foothold and the attacker's current position.
- Contain and investigate. Fold the finding into your incident response process — isolate the implicated host, hunt for the initial access vector, and assess what the attacker reached before tripping the wire.
- Feed it back. Every trip reveals attacker behavior. Use it to place new decoys where they will fire earlier next time and to tune your other detections.
The value of deception scales with the maturity of the response behind it. A tripwire nobody acts on is theater.
Where to start
Begin with honeytokens, because they are cheap, safe, and immediately useful. Plant a handful of fake credentials on high-value servers and in key config files, drop a canary document or two on your file shares, and wire each to an alert your monitoring team will actually see. Confirm the alerting path works end to end before you expand. Only once tokens are earning their keep should you consider decoy systems and honeynets, which demand real isolation engineering to deploy safely.
intSignal integrates deception into managed detection and response: honeytokens and decoys placed with attacker tradecraft in mind, wired into the same monitoring and response workflow that runs the rest of your detections. Talk to our security team and we will show you where a few well-placed traps would catch an intruder your current tools would miss.


